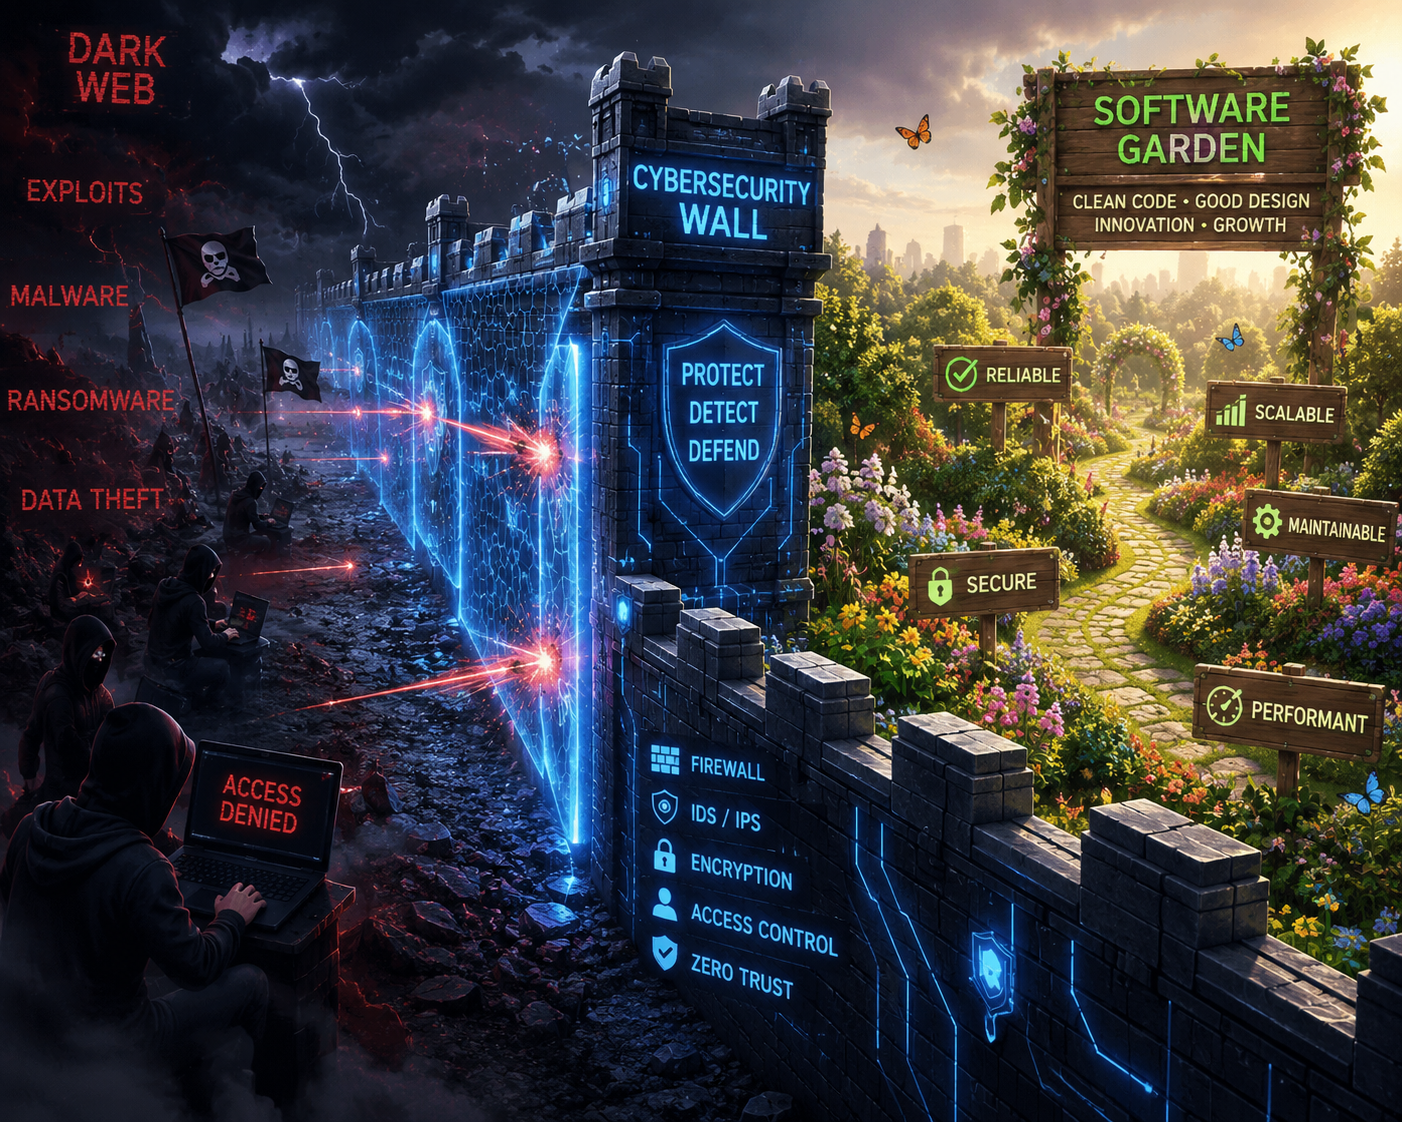
In today’s hyper-connected digital era, security is not a compliance feature—it is the bedrock of business resilience and customer trust. At Plotkai Interactive, we deliver enterprise-grade cybersecurity engineering, zero-trust network modeling, and continuous DevSecOps automation engineered to shield your applications, multi-cloud clusters, and proprietary data assets from highly sophisticated modern attack vectors.
Our Security Pillars & Engineering Expertise
Explore the comprehensive defensive and offensive capabilities we design, deploy, and govern.
Zero-Trust & SASE Modeling
Eliminate implicit trust. We construct perimeterless network topologies that dynamically verify every user, device, and request packet across your entire edge.
- ✔ Secure Access Service Edge (SASE) integration and perimeter microsegmentation
- ✔ Identity-Aware Proxies (IAP) and cloud tunnel configuration (Cloudflare Magic WAN)
- ✔ Real-time network telemetry audits and automated ingress/egress filtering
Cloud Security (CSPM & CWPP)
Harden multi-cloud environments. We deploy continuous posture scanning, automated misconfiguration remediation, and container runtime isolation.
- ✔ Cloud Security Posture Management (CSPM) mapping and drift detection
- ✔ Cloud Workload Protection Platforms (CWPP) inside Kubernetes (e.g., Wiz, Falco)
- ✔ Least-privilege Infrastructure Entitlement Management (CIEM) validation
Continuous DevSecOps
Inject safety at every git commit. We embed automated code, container, and dependency analysis gates into your deployment pipelines without slowing velocity.
- ✔ In-line SAST/DAST scanner orchestration and software supply chain audits (SBOM)
- ✔ Automated dependency vulnerability and license alerts (Snyk, Dependabot)
- ✔ Non-interactive secrets detection (TruffleHog) and automated KMS credential rotation
Threat Detection & Response
Establish centralized system-wide monitoring. We design high-throughput ingest frameworks that synthesize telemetry logs to isolate active anomalies.
- ✔ SIEM logging integration (Datadog Security, Elastic SIEM, Splunk)
- ✔ Automated SOAR workflows for dynamic network quarantine and credential revocation
- ✔ Proactive system-wide hunting and custom Sigma telemetry warning schemas
Offensive Pentesting & Red Teaming
Find weaknesses before attackers do. Our offensive security engineers simulate realistic adversary engagements, fuzz endpoints, and dissect software logic.
- ✔ Full-spectrum web application and REST/GraphQL API fuzzing
- ✔ Smart contract structural audits and decentralized infrastructure verification
- ✔ Targeted credential breach simulation, OSINT investigation, and threat profiling
Identity & Access Governance
Establish rigorous user boundary protocols. We deploy centralized single sign-on structures, privileged account shields, and temporal developer access.
- ✔ Enterprise Single Sign-On (SSO) with WebAuthn/FIDO2 phishing-resistant MFA
- ✔ Privileged Access Management (PAM) for ephemeral database and console credentialing
- ✔ Automated role lifecycle workflows and least-privilege attribute-based rules
Data Cryptography & DLP
Defend raw records from extraction. We design envelope-encryption schemes, configure secrets manager stores, and build zero-knowledge proof components.
- ✔ envelope-encryption using Hardware Security Modules (AWS KMS, GCP Cloud HSM)
- ✔ In-line Data Loss Prevention (DLP) to filter out sensitive PII/PHI payloads
- ✔ Zero-Knowledge (ZK) vault patterns keeping application host servers completely blind
GRC & Continuous Compliance
Streamline enterprise audit preparation. We translate complex security rules into automated policy controls, collecting proof indicators programmatically.
- ✔ SOC2 Type II, ISO 27001, HIPAA, GDPR, and PCI-DSS readiness frameworks
- ✔ Automated evidence collection and audit platforms mapping (Vanta, Drata)
- ✔ Continuous policy audits and automated risk-assessment registry logging
Proven Defensive Impact
Metrics achieved across our audited and hardened installations.
Our Security Hardening Roadmap
How we move your infrastructure from high risk to continuous compliance.
1. Threat Surface Assessment & Audit
We map your external attack perimeter, scan for active port vulnerabilities, analyze repository secrets leakages, and profile active endpoint access paths.
2. Policy-as-Code & Zero-Trust Blueprint
We design custom declarative IAM boundaries, construct secure edge network models, draft envelope-encryption policies, and map specific compliance requirements.
3. Continuous Pipeline Injection (DevSecOps)
We inject automated static code analysis, software supply chain auditing (SBOM), and container scanning directly into your automated deployment pipelines.
4. Telemetry Synthesis & Continuous Compliance
We configure centralized SIEM aggregation, deploy runtime security logs inside container systems, test warning triggers, and install continuous compliance tooling.
Let's Secure Your Digital Footprint
Is your engineering team prepping for a vital SOC2 audit, handling highly sensitive customer transaction workflows, or gearing up to onboard enterprise-level partners? Let our certified security architects perform a comprehensive Free Security Threat Audit of your infrastructure.